Friday, May 26, 2023

New Malware Used By SolarWinds Attackers Went Undetected For Years


The threat actor behind the supply chain compromise of SolarWinds has continued to expand its malware arsenal with new tools and techniques that were deployed in attacks as early as 2019, once indicative of the elusive nature of the campaigns and the adversary's ability to maintain persistent access for years.

According to cybersecurity firm CrowdStrike, which detailed the novel tactics adopted by the Nobelium hacking group last week, two sophisticated malware families were placed on victim systems — a Linux variant of GoldMax and a new implant dubbed TrailBlazer — long before the scale of the attacks came to light.

Nobelium, the Microsoft-assigned moniker for the SolarWinds intrusion in December 2020, is also tracked by the wider cybersecurity community under the names UNC2452 (FireEye), SolarStorm (Unit 42), StellarParticle (CrowdStrike), Dark Halo (Volexity), and Iron Ritual (Secureworks).

The malicious activities have since been attributed to a Russian state-sponsored actor called APT29 (also known as The Dukes and Cozy Bear), a cyber espionage operation associated with the country's Foreign Intelligence Service that's known to be active since at least 2008.

GoldMax (aka SUNSHUTTLE), which was discovered by Microsoft and FireEye (now Mandiant) in March 2021, is a Golang-based malware that acts as a command-and-control backdoor, establishing a secure connection with a remote server to execute arbitrary commands on the compromised machine.

Mandiant also pointed out that Dark Halo actors had used the malware in attacks going back to at least August 2020, or four months before SolarWinds discovered its Orion updates had been tampered with malware designed to drop post-compromise implants against thousands of its customers.

In September 2021, Kaspersky revealed details of a second variant of the GoldMax backdoor called Tomiris that was deployed against several government organizations in an unnamed CIS member state in December 2020 and January 2021.

The latest iteration is a previously undocumented but functionally identical Linux implementation of the second-stage malware that was installed in victim environments in mid-2019, predating all other identified samples built for the Windows platform to date.


Also delivered around the same timeframe was TrailBlazer, a modular backdoor that offers attackers a path to cyber espionage, while sharing commonalities with GoldMax in the way it masquerades its command-and-control (C2) traffic as legitimate Google Notifications HTTP requests.

Other uncommon channels used by the actor to facilitate the attacks include —

  • Credential hopping for obscuring lateral movement
  • Office 365 (O365) Service Principal and Application hijacking, impersonation, and manipulation, and
  • Theft of browser cookies for bypassing multi-factor authentication

Additionally, the operators carried out multiple instances of domain credential theft months apart, each time leveraging a different technique, one among them being the use of Mimikatz password stealer in-memory, from an already compromised host to ensure access for extended periods of time.

"The StellarParticle campaign, associated with the Cozy Bear adversary group, demonstrates this threat actor's extensive knowledge of Windows and Linux operating systems, Microsoft Azure, O365, and Active Directory, and their patience and covert skill set to stay undetected for months — and in some cases, years," the researchers said.

Related posts


RFCrack Release - A Software Defined Radio Attack Tool

RFCrack uses the following hardware with RFCat libraries:
YardStick One: 
https://goo.gl/wd88sr

I decided to cleanup my RF testing harness and release it as a tool named RFCrack
Mostly because it has been pain to set up use-case scenarios from scratch for every device I am testing. Rather then release a tool no one knows how to use. The below video will be a quick but comprehensive tutorial to get you started If you've been following the blogs, this will greatly simplify your testing, in the following ways:
  • RFCrack handles all of your data conversions. 
  • It allows you to capture, replay and save payloads for use anytime 
  • It will handle rolling code bypass attacks on your devices. 
  • You can jam frequencies and fuzz specific values 
  • It will also allow you to scan specific frequencies in discovery mode or incrementally probe them 
  • RFCrack will hopefully have keyless entry & engine bypass support in the near future

This is the first release, everything works as intended but there will be plenty of updates as I continue to do research and find reasons to add features needed for testing. I am still making changes and making it more flexible with modifiable values and restructuring code.  If you have any legitimate use case scenarios or need a specific value to be modifiable, hit me up and I will do my best to update between research, if its a legitimate use case.

You can reach me at:
Twitter: @Ficti0n
http://cclabs.io , http://consolecowboys.com

GitHub Code for RFCrack:

https://github.com/cclabsInc/RFCrack

Full RF Hacking Course in Development:

Not all of the attacks in the tool have been covered in the RF hacking blog series and a few more are in research mode, as such, not yet added to the tool but will probably be covered in a full length online class on Hacking with RF which includes all targets and equipment.  Send an email to info(at)cclabs.io if your interested.


Walkthrough Training Video:


Until Next time: 

Cheers, and enjoy the tool for your personal use testing devices, feedback and bug reports are appreciated.  I have another RF blog coming out shortly based on my friends research into hacking garages/gates and creating keyfobs.  I will post when its ready. 
More info
  1. Hacker Security Tools
  2. Hacking Apps
  3. Nsa Hack Tools
  4. Hack Tools For Pc
  5. What Are Hacking Tools
  6. Beginner Hacker Tools
  7. Hacker Tools Mac
  8. Pentest Tools Open Source
  9. Hacker Techniques Tools And Incident Handling
  10. Hack Tools Pc
  11. Hacking Tools Free Download
  12. Pentest Tools Github
  13. Hack Tools For Ubuntu
  14. Hacker Tools Software
  15. Pentest Tools Review
  16. Hack And Tools
  17. Best Pentesting Tools 2018
  18. Pentest Tools Website
  19. Hack Website Online Tool
  20. Hack Tools Download
  21. Pentest Tools Free
  22. Hacker Tools Github
  23. How To Install Pentest Tools In Ubuntu
  24. Best Pentesting Tools 2018
  25. Install Pentest Tools Ubuntu
  26. Best Hacking Tools 2019
  27. Pentest Tools Tcp Port Scanner
  28. Hacks And Tools
  29. Hacker Tools
  30. Pentest Tools Find Subdomains
  31. Hack Tools For Pc
  32. Pentest Tools Download
  33. Hacking Tools Online
  34. Hacking Tools Download
  35. Hacker Tools 2020
  36. Pentest Tools For Windows
  37. Pentest Tools Apk
  38. Hacking Tools For Windows
  39. Hack And Tools
  40. How To Hack
  41. Blackhat Hacker Tools
  42. Blackhat Hacker Tools
  43. Nsa Hacker Tools
  44. Hacking Tools For Kali Linux
  45. Pentest Tools Port Scanner
  46. How To Install Pentest Tools In Ubuntu
  47. Beginner Hacker Tools
  48. Hacking App
  49. Pentest Tools Android
  50. Hacker Tools For Mac
  51. Game Hacking
  52. Hacking Tools For Mac
  53. What Are Hacking Tools
  54. Hacker Tools For Windows
  55. Hacker Tools Linux
  56. Underground Hacker Sites
  57. Black Hat Hacker Tools
  58. Pentest Automation Tools
  59. Pentest Tools Free
  60. Pentest Tools Github
  61. Top Pentest Tools
  62. Hacking Tools Download
  63. Hacker Tools Free
  64. Best Hacking Tools 2020
  65. Game Hacking
  66. Pentest Tools For Ubuntu
  67. Game Hacking
  68. Hacking Tools Windows
  69. Hackrf Tools
  70. Hack Tools Github
  71. Hacker Tools 2019
  72. Hacking App
  73. Pentest Tools For Ubuntu
  74. Hacking Tools For Windows
  75. Pentest Tools Github
  76. Pentest Tools For Windows
  77. Pentest Tools Subdomain
  78. What Is Hacking Tools
  79. Hack Tools For Ubuntu
  80. Pentest Tools Review
  81. Hack Tools For Windows
  82. Hacking Tools Software
  83. Hack And Tools
  84. Hacker Tools Apk
  85. Wifi Hacker Tools For Windows
  86. Hacking Tools Windows
  87. Pentest Tools Apk
  88. Pentest Tools Kali Linux
  89. Hack Apps
  90. Hacker Tools Windows
  91. Hacker Tools Apk
  92. Hacker Tool Kit
  93. Hacker Tools For Ios
  94. Hacking Tools Download
  95. Hacker Tools Software
  96. Hack Tools
  97. Hacker Tool Kit
  98. Hack Tools Pc
  99. Hacking Tools Hardware
  100. Easy Hack Tools
  101. Hacking Tools Pc
  102. Hacker Tools
  103. Pentest Tools Website Vulnerability
  104. Hacking Tools Software
  105. Hacking Tools And Software
  106. Nsa Hacker Tools
  107. Hack Apps
  108. Pentest Tools Url Fuzzer
  109. Hacking Tools Download
  110. Hack Tools Github
  111. Hacker Security Tools
  112. Hack Tool Apk No Root
  113. Hacks And Tools
  114. Bluetooth Hacking Tools Kali
  115. Hacker Tools Free
  116. Growth Hacker Tools
  117. Hack Tools
  118. Top Pentest Tools
  119. Hacking Tools For Mac
  120. Hack Tools For Mac
  121. Hacking Tools Windows 10
  122. Nsa Hack Tools Download
  123. Hacker Tools Free
  124. Wifi Hacker Tools For Windows
  125. Computer Hacker
  126. How To Hack
  127. Nsa Hack Tools
  128. Hacker Tools
  129. Hacker Tools
  130. Kik Hack Tools
  131. Usb Pentest Tools
  132. Blackhat Hacker Tools
  133. Hacking Tools For Beginners
  134. Hack Tools Download
  135. Hacker Tools For Pc
  136. Tools Used For Hacking
  137. Hacking App
  138. Pentest Tools For Android
  139. Hack And Tools
  140. Hack Website Online Tool
  141. New Hacker Tools
  142. Hack Tool Apk
  143. Hacker Tools Github
  144. Hacking Tools For Beginners
  145. Hacking Tools Name
  146. Pentest Tools Nmap
  147. Hacker Tools Free Download
  148. What Are Hacking Tools
  149. Kik Hack Tools
  150. Best Hacking Tools 2020
  151. Pentest Tools Open Source
  152. Nsa Hack Tools
  153. Pentest Tools Framework
  154. Hacker Tools Apk
  155. Pentest Tools For Mac
  156. Pentest Tools List
  157. Pentest Tools Apk
  158. World No 1 Hacker Software
  159. Hacking Tools Windows
  160. Hacker Tools For Windows
  161. Hack Website Online Tool
  162. Hacking Apps
  163. Hacking Apps
  164. Pentest Tools For Android
  165. Hacker Tools For Windows
  166. Hack Tools For Windows
  167. Growth Hacker Tools
  168. Hack Rom Tools
  169. Hack Tools Pc

Recovering Data From An Old Encrypted Time Machine Backup

Recovering data from a backup should be an easy thing to do. At least this is what you expect. Yesterday I had a problem which should have been easy to solve, but it was not. I hope this blog post can help others who face the same problem.


The problem

1. I had an encrypted Time Machine backup which was not used for months
2. This backup was not on an official Apple Time Capsule or on a USB HDD, but on a WD MyCloud NAS
3. I needed files from this backup
4. After running out of time I only had SSH access to the macOS, no GUI

The struggle

By default, Time Machine is one of the best and easiest backup solution I have seen. As long as you stick to the default use case, where you have one active backup disk, life is pink and happy. But this was not my case.

As always, I started to Google what shall I do. One of the first options recommended that I add the backup disk to Time Machine, and it will automagically show the backup snapshots from the old backup. Instead of this, it did not show the old snapshots but started to create a new backup. Panic button has been pressed, backup canceled, back to Google.


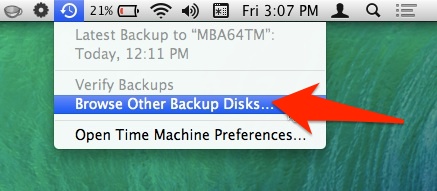
Other tutorials recommend to click on the Time Machine icon and pressing alt (Option) key, where I can choose "Browse other backup disks". But this did not list the old Time Machine backup. It did list the backup when selecting disks in Time Machine preferences, but I already tried and failed that way.


YAT (yet another tutorial) recommended to SSH into the NAS, and browse the backup disk, as it is just a simple directory where I can see all the files. But all the files inside where just a bunch of nonsense, no real directory structure.

YAT (yet another tutorial) recommended that I can just easily browse the content of the backup from the Finder by double-clicking on the sparse bundle file. After clicking on it, I can see the disk image on the left part of the Finder, attached as a new disk.
Well, this is true, but because of some bug, when you connect to the Time Capsule, you don't see the sparse bundle file. And I got inconsistent results, for the WD NAS, double-clicking on the sparse bundle did nothing. For the Time Capsule, it did work.
At this point, I had to leave the location where the backup was present, and I only had remote SSH access. You know, if you can't solve a problem, let's complicate things by restrict yourself in solutions.

Finally, I tried to check out some data forensics blogs, and besides some expensive tools, I could find the solution.

The solution

Finally, a blog post provided the real solution - hdiutil.
The best part of hdiutil is that you can provide the read-only flag to it. This can be very awesome when it comes to forensics acquisition.


To mount any NAS via SMB:
mount_smbfs afp://<username>@<NAS_IP>/<Share_for_backup> /<mountpoint>

To mount a Time Capsule share via AFP:
mount_afp afp://any_username:password@<Time_Capsule_IP>/<Share_for_backup> /<mountpoint>

And finally this command should do the job:
hdiutil attach test.sparsebundle -readonly

It is nice that you can provide read-only parameter.

If the backup was encrypted and you don't want to provide the password in a password prompt, use the following:
printf '%s' 'CorrectHorseBatteryStaple' | hdiutil attach test.sparsebundle -stdinpass -readonly

Note: if you receive the error "resource temporarily unavailable", probably another machine is backing up to the device

And now, you can find your backup disk under /Volumes. Happy restoring!

Probably it would have been quicker to either enable the remote GUI, or to physically travel to the system and login locally, but that would spoil the fun.

Related posts


  1. Hacking Tools For Pc
  2. Hacking Tools For Windows
  3. Install Pentest Tools Ubuntu
  4. Hacking Apps
  5. Hack Tools For Windows
  6. Pentest Tools Port Scanner
  7. Usb Pentest Tools
  8. Termux Hacking Tools 2019
  9. Hacker Tool Kit
  10. Hacking Tools 2019
  11. Hacking Tools For Windows Free Download
  12. Hacker Tools Hardware
  13. Hacker Tools For Windows
  14. Hacker Tools For Ios
  15. Pentest Tools Free
  16. Hack Tools For Ubuntu
  17. Pentest Box Tools Download
  18. Pentest Tools For Windows
  19. Pentest Recon Tools
  20. Hacking Tools For Beginners
  21. Hacker Tools Hardware
  22. Pentest Box Tools Download
  23. Hacker Tools Apk Download
  24. Hack Rom Tools
  25. Hacking Tools For Pc
  26. Hacking App
  27. Pentest Tools Free
  28. Hack App
  29. Hacker Tools For Ios
  30. Hacking Tools Windows 10
  31. Hacks And Tools
  32. Hack Tools Online
  33. Free Pentest Tools For Windows
  34. Blackhat Hacker Tools
  35. Hacker Tools Online
  36. Hacker Tools 2020
  37. Hacks And Tools
  38. Hacker Tools Online
  39. Hak5 Tools
  40. Pentest Tools Free
  41. Hacking Tools Pc
  42. Hack Website Online Tool
  43. New Hacker Tools
  44. Hack App
  45. Hacker Tools Free
  46. Hack Tools For Ubuntu
  47. Hacking Tools For Mac
  48. Hacker Tools Windows
  49. Hacking Tools For Pc
  50. Android Hack Tools Github
  51. Pentest Tools Online
  52. Hackrf Tools
  53. Pentest Automation Tools
  54. Pentest Tools Alternative
  55. How To Hack
  56. Android Hack Tools Github
  57. Pentest Tools Windows
  58. Hack App
  59. Hacking Tools Software
  60. Hacking Tools Free Download
  61. Hacker Search Tools
  62. Pentest Tools Nmap
  63. Android Hack Tools Github
  64. Hacker Techniques Tools And Incident Handling
  65. Hacker Tools For Ios
  66. Pentest Tools Github
  67. Pentest Tools List
  68. Hacking Tools Mac
  69. New Hacker Tools
  70. Tools Used For Hacking
  71. Ethical Hacker Tools
  72. Tools Used For Hacking
  73. Pentest Tools Apk
  74. Pentest Tools For Android
  75. Pentest Automation Tools
  76. Pentest Tools Nmap
  77. Free Pentest Tools For Windows
  78. Wifi Hacker Tools For Windows
  79. Github Hacking Tools
  80. Best Pentesting Tools 2018
  81. Pentest Tools Nmap
  82. Hacking App
  83. Pentest Tools For Windows
  84. Hacker Search Tools
  85. Best Pentesting Tools 2018
  86. Hackers Toolbox
  87. Nsa Hack Tools
  88. Pentest Recon Tools
  89. Hacker Tools Online
  90. Hack Tool Apk No Root
  91. Hacking Tools For Windows
  92. Best Hacking Tools 2020
  93. Install Pentest Tools Ubuntu
  94. Hacking Tools Hardware
  95. Pentest Tools Nmap
  96. Hacker Tools Linux
  97. Hacking Tools For Games
  98. Hacking Tools Usb
  99. Free Pentest Tools For Windows
  100. Hack Tools
  101. Hack Tools Online
  102. How To Make Hacking Tools
  103. Bluetooth Hacking Tools Kali
  104. Hacking Tools 2020
  105. Hacking Apps
  106. Hacker Tools For Ios
  107. Hack And Tools
  108. Hacking Tools And Software
  109. Hack Tools Download
  110. Tools For Hacker
  111. Hacker Tool Kit
  112. Kik Hack Tools
  113. Hack Tools Online
  114. Pentest Tools Framework
  115. Pentest Tools For Ubuntu
  116. Pentest Tools Open Source
  117. Pentest Recon Tools
  118. Hack Apps
  119. Hacker Tools 2019
  120. Pentest Tools Framework
  121. Pentest Tools Subdomain
  122. How To Hack
  123. Hacks And Tools
  124. Hack Tools For Games
  125. Beginner Hacker Tools
  126. How To Make Hacking Tools
  127. Hacker Tools Online
  128. How To Install Pentest Tools In Ubuntu
  129. Pentest Tools Windows

Thursday, May 25, 2023

BurpSuite Introduction & Installation


What is BurpSuite?
Burp Suite is a Java based Web Penetration Testing framework. It has become an industry standard suite of tools used by information security professionals. Burp Suite helps you identify vulnerabilities and verify attack vectors that are affecting web applications. Because of its popularity and breadth as well as depth of features, we have created this useful page as a collection of Burp Suite knowledge and information.

In its simplest form, Burp Suite can be classified as an Interception Proxy. While browsing their target application, a penetration tester can configure their internet browser to route traffic through the Burp Suite proxy server. Burp Suite then acts as a (sort of) Man In The Middle by capturing and analyzing each request to and from the target web application so that they can be analyzed.


Everyone has their favorite security tools, but when it comes to mobile and web applications I've always found myself looking BurpSuite . It always seems to have everything I need and for folks just getting started with web application testing it can be a challenge putting all of the pieces together. I'm just going to go through the installation to paint a good picture of how to get it up quickly.

BurpSuite is freely available with everything you need to get started and when you're ready to cut the leash, the professional version has some handy tools that can make the whole process a little bit easier. I'll also go through how to install FoxyProxy which makes it much easier to change your proxy setup, but we'll get into that a little later.

Requirements and assumptions:

Mozilla Firefox 3.1 or Later Knowledge of Firefox Add-ons and installation The Java Runtime Environment installed

Download BurpSuite from http://portswigger.net/burp/download.htmland make a note of where you save it.

on for Firefox from   https://addons.mozilla.org/en-US/firefox/addon/foxyproxy-standard/


If this is your first time running the JAR file, it may take a minute or two to load, so be patient and wait.


Video for setup and installation.


You need to install compatible version of java , So that you can run BurpSuite.
Related word

Where Have We Been?

 As you can see, this blog has been dormant for a little over two years. You would think that the pandemic would have given me more time for reviewing games, and maybe it has, but I have been lacking in motivation.

Oddly, the shuttering of Google Plus put a large dent in my website traffic numbers (I may have been one of the few people who was benefiting from it), but mostly it has seemed like there are more important things going on in the world than board game reviews, and I thought the best way I could help would be to get out of the way and stop contributing to the noise.

Now that the world has calmed down a little bit (has it though?) I hope to get back to sharing my random thoughts on my admittedly trivial hobby. Stay tuned...